The Imperative of Continuous Verification in Micro-Segmented Environments
Zero Trust architecture dictates an uncompromising rule: "Never Trust, Always Verify." Under this security model, continuous verification is not merely an access control mechanism—it demands persistent, round-the-clock packet capture and pervasive analytical inspection across every single layer of the network.
Beyond Perimeter Security: Taming Lateral Vulnerabilities
Traditional legacy security perimeter architectures focused overwhelmingly on North-South visibility—traffic entering and leaving through boundary firewalls. However, modern attacks exploit this blind spot by penetrating edge defenses and moving laterally inside the datacenter through East-West vectors. Implementing micro-segmentation divides networks into isolated zones, but without active traffic interception, micro-segment boundaries become impenetrable black boxes.
To establish true Zero Trust network visibility, security architects must deploy an out-of-band monitoring fabric capable of extracting full fidelity packets directly from physical lines, virtual switches, and micro-perimeters without inducing latency or system fragility.
▶ Total Telemetry Extraction
Raw packet data provides immutable ground truth. Unlike summarized NetFlow/IPFIX, raw payloads captured via hardware TAPs expose evasive multi-stage lateral exploits and zero-day protocol anomalies.
▶ Decoupled Security from Production
By leveraging Network Packet Brokers (NPB) alongside physical and virtual TAPs, analytical appliances receive targeted streams out-of-band without degrading operational inline workloads.
Architecting Zero Blind Spots: TAPs and Packet Brokers
Deploying physical and virtual Test Access Points (TAPs) paired with advanced Network Packet Brokers establishes the deterministic physical foundation necessary for continuous micro-segmentation visibility.
Physical & Virtual TAPs
Network TAPs mirror raw optical and copper line signals at the lowest physical layers, ensuring non-intrusive traffic duplication with zero packet drop. In software-defined and micro-segmented architectures, hypervisor-level virtual TAPs extract inter-VM and inter-container East-West communications without burdening CPU processing cycles.
Intelligent Traffic Aggregation
Micro-segmentation generates hundreds of disparate monitoring endpoints. A high-performance micro-segmentation packet broker unifies these isolated feeds, aggregating hundreds of gigabits of distributed East-West traffic into unified, manageable analysis pipelines for enterprise SOC teams.
Optimization & Tool Offloading
Downstream security tooling (IDS, SIEM, APM, NDR) quickly saturates under massive full-line data rates. Network Packet Brokers perform critical hardware-level preprocessing: deduplication, Layer 2-7 packet filtering, packet slicing, payload masking, and nanosecond timestamping to dramatically optimize tool efficiency.
Full-Spectrum East-West Traffic Monitoring
East-West traffic monitoring inside a Zero Trust domain poses unique challenges: encrypted micro-service transactions, high-volume container communications, and transient hybrid cloud instances. Deploying dedicated TAP points ensures that all intra-zone flows are duplicated directly at their source.
The centralized NPB then intelligently filters out unneeded analytical overhead, decapsulates overlay encapsulations (such as VXLAN, NVGRE, or GENEVE), and transmits precisely targeted packet flows to Intrusion Detection Systems (IDS) and Network Performance Monitors (NPM).
✔ Continuous Identity & Flow Validation
Real-time correlation of granular flow records with container and user identities across ephemeral zones to validate least-privilege policies at runtime.
⚠ Rapid Micro-Breach Containment
Detecting lateral infiltration within seconds by feeding deep packet inspection (DPI) engines high-precision captures from segment boundaries.
Who we are?
Mylinking is a wholly-owned subsidiary of Transworld, which is a leading provider in the TV/Radio Broadcasting & Telecommunication industry with extensive operational experience since 2008.
Moreover, Mylinking specializes in Network Traffic Visibility, Network Data Visibility, and Network Packet Visibility. Our purpose-built platforms Capture, Replicate, and Aggregate Inline or Out-of-Band network data traffic without packet loss, guaranteeing the delivery of the Right Packets to the Right Tools—including IDS, APM, NPM, and forensic systems—for comprehensive Network Monitoring, Advanced Analysis, and Zero Trust Network Security.
What can we do?
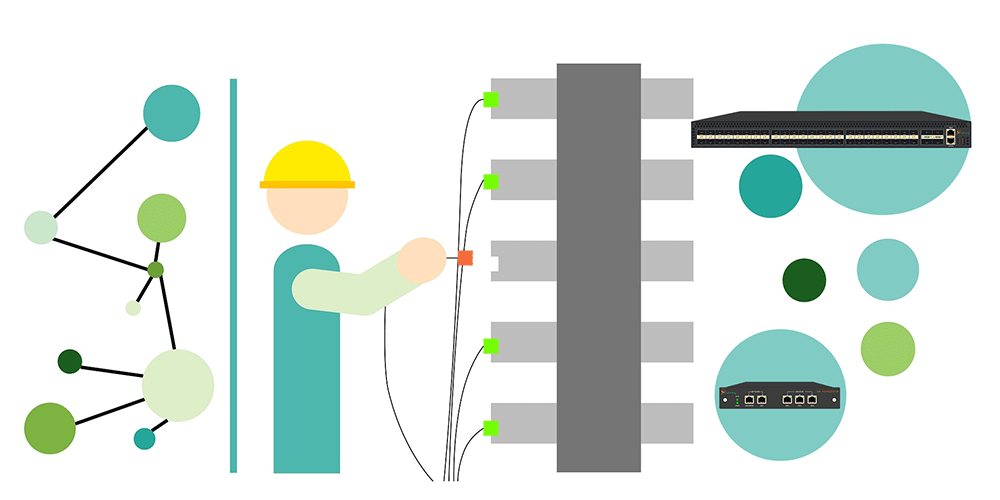
Enterprise solutions for comprehensive network data visibility across diverse mission-critical infrastructures.
Comprehensive Packet Broker & TAP Capabilities
Based on cutting-edge Traffic Capture, Replication, Aggregation, Packet Filtering, Slicing, Masking, Deduplication, and Timestamping Technologies of Network Tap, Network Packet Broker, and Inline Bypass Switch, we provide a one-stop solution for Network Monitoring and Network Security in Data Center, Cloud Platform, Big Data, Telecom Operator, TV Broadcasting, Government, Education, IT, Finance, Bank, Hospital, Transportation, Energy, Power, Petroleum, Enterprise and other industries. And also involve CCTV, CATV, IPTV, HFC, DTH & Radio Integration Solution, and FTTC/FTTB/FTTH, EPON/GPON, WLAN, Wi-Fi, RF, Bluetooth Distribution & Transmission.
Our Strong Technology
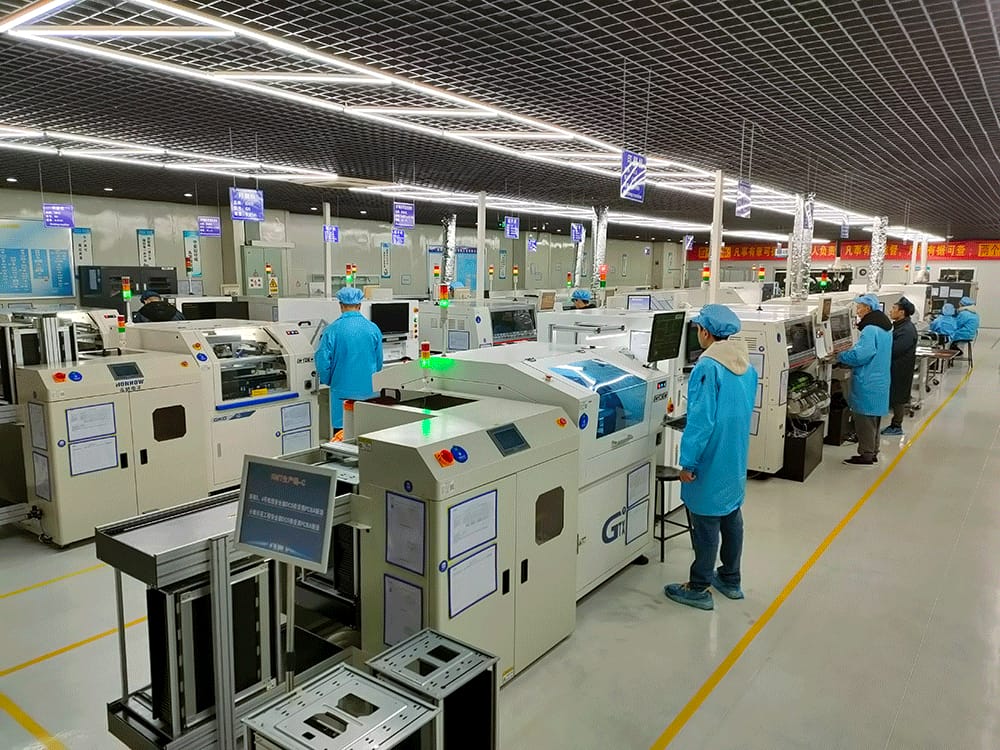
With technique innovation, customizable design, and strong service support, all of our products comply with international quality standards, and are greatly appreciated in a variety of different markets throughout the world.
Persisting to the principle of "making trade services the forerunner of our business", we always strive for high efficiency, passion, integrity & good faith to maintain our customers' loyalty, to meet our customers' satisfaction by our commitment to excellence.
Our solutions empower network architects to reliably construct high-density TAP fabrics, eliminate monitoring blind spots across dynamic micro-segments, and achieve flawless packet routing for real-time security verification engines.
Strategic Implementation: Deploying Across Micro-Segments
A step-by-step approach to unifying your TAP and Packet Broker architecture with enterprise Zero Trust requirements.
Mapping Critical Segments
Audit inter-VLAN, inter-rack, and cloud tenant East-West communication pathways. Establish deterministic tap locations at core, aggregation, and software hypervisor virtual switches to monitor all lateral flows without altering path topologies.
Decoupling Traffic Collection
Aggregate distributed mirror and TAP links onto unified high-density Network Packet Brokers. Route traffic safely away from production lines to maintain ultra-low latency while eliminating inline bottlenecks on primary switching fabrics.
Dynamic Security Orchestration
Deliver pre-filtered, decrypted, and de-duplicated packet streams dynamically to SIEM, NDR, and continuous verification analytical clusters, ensuring 100% blind-spot-free threat detection under any scale.
-

Tel
-

E-mail
-

Skype
-

Top